Skip to content

Every high-risk agent action, held until it is released.

ActEscrow puts a gateway you own in front of your ERP and finance APIs. An AI agent's bank-account change or invoice approval waits there until policy and two independent approvers release that exact action. Then it runs once, and leaves a receipt anyone can verify offline.

See how release works

EU-first engineering pilot · seeking paid design partners · User manual · FAQ

Escrow instrumentNo. 7F3A-91C2
Agent
agt-invoice-01
Action
erp.supplier.bank_account.change
Change
SUP-1001 · new IBAN SE45 5000 0000 0583 9825 7466
Digest
sha256:7f3a91c2…e04b
SHA-256 · 7F3A91C2 … E04B · SEALED ACTION DIGEST ·Held1 of 2 signed

Approver 1 · Finance

Signed 09:42

Approver 2 · Treasury

Awaiting signature

Held — 1 of 2 signatures

Illustrative instrument with synthetic data — the real one is your approvals inbox.
Zero agent ERP keys
Agents hold an OIDC caller identity only; your gateway alone holds target credentials.
Fail closed, then reconcile
When the control plane is down, protected writes stop. Timeouts become Unknown until verified.
Hash chain + ECDSA P-256
Append-only PostgreSQL log under row-level security, rotated checkpoints, offline CLI verification.
Tested at the boundaries
Integration suites cover separation of duties, receipts, row-level security and cross-tenant isolation.

Four conditions stand between an agent and a payment.

Prompt guardrails and agent registries describe intent. ActEscrow controls the moment of execution — and keeps the proof.

  1. Held at your gateway

    The agent calls a gateway you run. It never holds ERP or payment credentials, so there is no path around the hold.

    • Per-agent scope & minor-unit amount limits checked before deterministic policy evaluation
    • SHA-256 canonical intent digest, justification, and notAfter deadline bind each proposal
    • Fail-closed 503 on outage; Unknown and Conflict outcomes halt blind retries
  2. Released by two signatures

    Policy decides; where it requires people, two independent approvers sign the exact action — its digest, not a summary.

    • Blocks self-approval by agent owners and RFC 8693 act-claim delegators
    • Enforces WebAuthn / MFA acr & amr claims on Approver and TenantAdmin decisions
    • Kill-switch cancellation, durable exception tracking, and clean vote revocation
  3. Executed exactly once

    Redeem moves Approved to Executing once. If the outcome is uncertain, the action is held as Unknown and reconciled, never retried blindly.

    • At-most-once redeem bound to the approved digest
    • Read-back verification: a contradicting ERP state is a Conflict, never a success
    • Control plane unavailable → the gateway fails closed with 503
  4. Proven offline

    Every step lands in an append-only, hash-chained evidence log. Receipts and exports verify without trusting us.

    • PII-free receipts (aa.receipt.v1) & ECDSA P-256 checkpoints via local or KMS/HSM signer
    • Signed tenant export bundles verified offline with aa-verify receipt & aa-verify bundle
    • SSRF-hardened SIEM push, dual-admin legal holds, and chain-preserving tenant offboarding

Try to get a payment past the gateway.

Inspect how the customer-owned gateway handles normal dual-control execution, tampered parameters, control-plane outages, and direct ERP bypasses.

1. Supplier Bank Change

Agent requests an IBAN update through the customer gateway. Execution blocks until two independent MFA-verified humans approve the exact SHA-256 digest.

Dual Control + Verified
  1. AgentOK

    OIDC token only

  2. GatewayOK

    Digest + lease redeemed

  3. Control PlaneOK

    RequireApproval (2)

  4. ApproversOK

    2 MFA votes + SoD

  5. Target ERPOK

    Executed once + verified

Inbound request

POST /v1/actions
Idempotency-Key: ac-8f3c1e
tool: erp.supplier.bank_account.change
resource: supplier:SUP-1001
iban: DE89370400440532013000

Gateway decision (202 -> 200 OK)

HTTP 202 PendingApproval -> HTTP 200 Executed
downstreamVerified: true
targetReference: CHG-9a14f20b1c88
execCount: 1 (single-use lease redeemed)

Recorded hash-chained evidence trace

  1. 1.action.evaluated (RequireApproval)
  2. 2.approval.recorded (approver_1, acr=mfa)
  3. 3.approval.recorded (approver_2, SoD passed)
  4. 4.action.approved (policyRev=1)
  5. 5.execution.redeemed (single-use lease)
  6. 6.execution.outcome (downstreamVerified=true)

Invariant: Agent owner and RFC 8693 act delegator are both blocked from self-approval.

A production-shaped core on open standards.

Built with .NET 10 LTS, PostgreSQL 18 with row-level security, Keycloak 26 (OIDC, WebAuthn), Next.js 16 and OpenTelemetry, in non-root chiseled containers.

Where each part runs

Customer-Owned Gateway

Azure · AWS · GCP · On-Prem

Holds target API keys locally; outbound HTTPS only to the control plane.

Status: Always required for real enforcement

EU Pilot Control Plane (single VPS)

Docker Compose behind TLS

Lean single-node pilot stack for the SaaS side (~€20–€150 infra envelope).

Status: Pilot stack live at actescrow.com · single node, not HA

Managed EU Cloud (Azure / AWS / GCP)

Container Apps / ECS / Cloud Run + Managed Postgres

PITR backups, Vault/KMS custody, zone redundancy, and enterprise procurement readiness.

Status: Commercial scale profile (R23)

Capability register

  • erp.supplier.bank_account.change

    Two-person SoD approval bound to normalized IBAN, BIC & account holder with read-back ERP verification.

    Verified Slice
  • erp.invoice.approve

    Threshold-driven maker-checker approvals bound to exact minor units, currency & invoice reference.

    Verified Slice
  • Per-Agent Scope & Amount Limits

    Tool/resource pattern rules and minor-unit currency caps evaluated before policy; maker-checker on scope changes.

    Enforced (R24)
  • Conflict & Exception Cases

    Contradicting read-back enters Conflict; timeouts enter Unknown; durable exception cases block blind retries.

    Reconciled (R26/R28)
  • Signed Receipts & Export Bundles

    PII-free aa.receipt.v1, tenant export bundles, pluggable KMS/HSM IAnchorSigner, and offline aa-verify CLI.

    Verifiable (R27/R31)
  • Postgres 18 RLS + Offboarding

    aa_app cannot UPDATE/DELETE ledger rows; dual-admin offboarding redacts PII while keeping chains verifiable.

    Hardened (R31)
  • OpenTelemetry + Prometheus Counters

    Per-gateway decision metrics, trace correlation IDs, liveness/readiness checks, and operational runbooks.

    Observable

Enforcement happens inside your network — never by agent honor system

HTTPS · mTLS-ready · Zero direct ERP keys
AI Agent RuntimeAzure · AWS · GCPn8n · .NET · Python · MCPCustomer GatewayCanonical SHA-256 digestRFC 8693 act delegationHolds ERP secrets · At-most-onceEU Control PlaneAgent Scope · Policy · SoDSingle-use Leases · RLS LedgerNamed Human Approvers (MFA / WebAuthn)Justification & deadline · Reject or RevokeTarget ERP / Finance APIExecuted once + read-back verifiedEvidence VaultReceipts + P-256 CheckpointsKMS/HSM · aa-verify CLI

Execution safety: an at-most-once state machine

No Blind Retries
Approved LeaseSingle-use · notAfterGateway + Read-BackExecute once & verify stateSucceeded (Verified)Signed aa.receipt.v1 emittedUnknown (Ambiguous)Reconcile before any retryConflict (HTTP 409)Exception case · human review

Portable cryptographic proof

PII-Free
Action + Policy + VotesIDs, digests & states onlyIAnchorSigner (P-256)Local key or KMS / HSM HTTPSigned Artifactsaa.receipt.v1 (per action)Tenant Export BundleSHA-256 chain + checkpointsaa-verify CLIaa-verify receiptaa-verify bundleOffline · Retired-key aware

The inbox, the conflict review and the vault.

Real screens from the console. The user manual walks through all of them with annotated screenshots.

Open the user manual
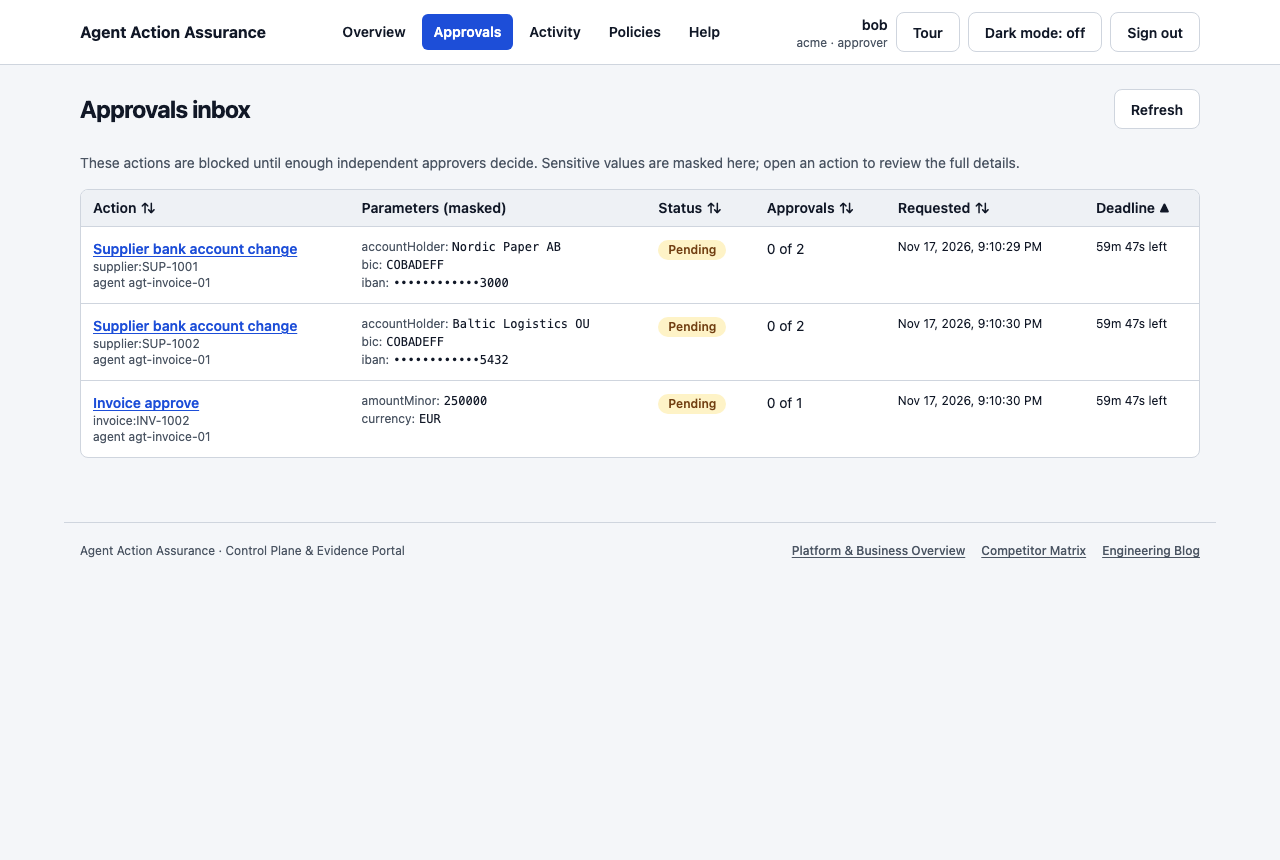
Approvals inbox showing pending high-risk agent actions

Approvals Inbox

Pending dual-control requests with risk tier, deadline, and SoD eligibility.

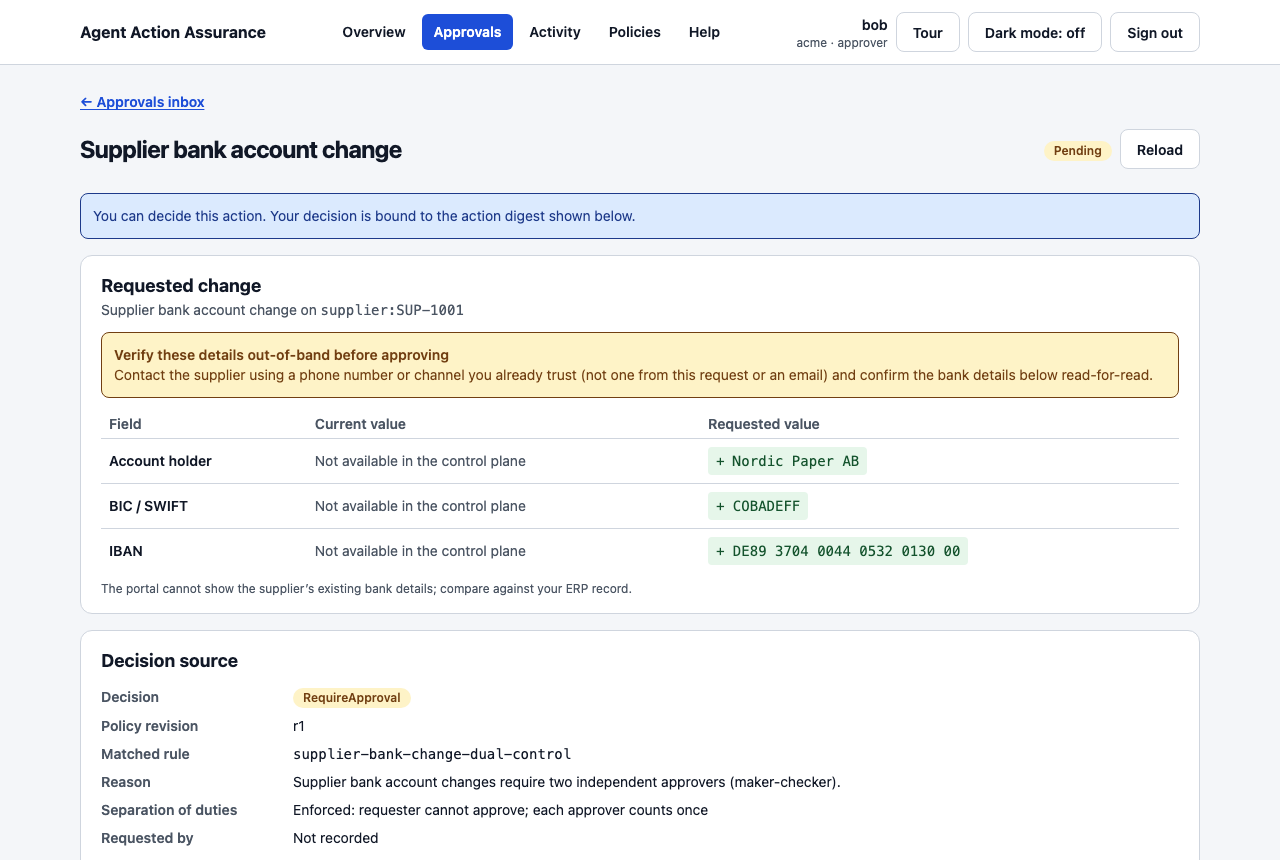
Action detail showing requested change, justification, and digest

Action Detail & Justification

Canonical parameter diff, agent justification, notAfter window, and digest.

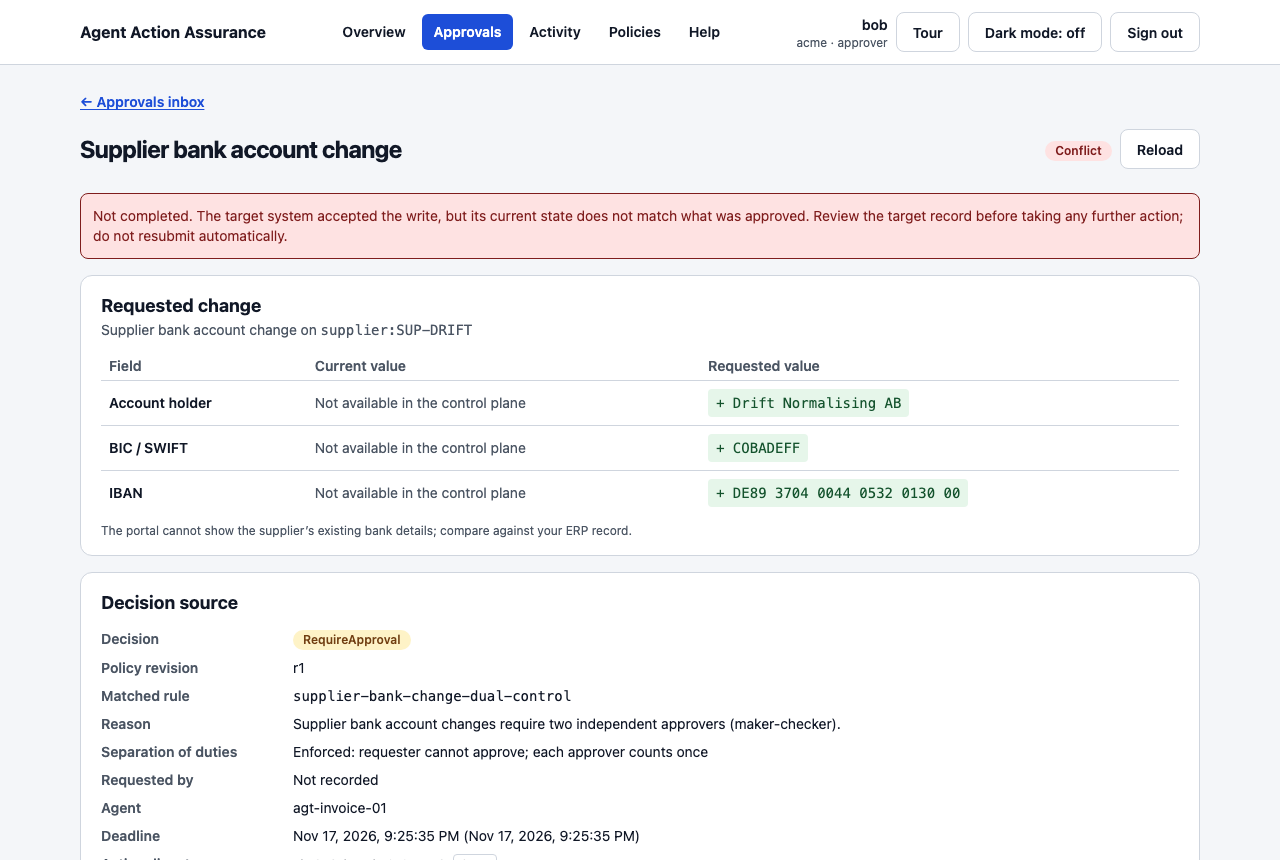
Conflict action detail showing read-back mismatch

Conflict Read-Back Review

Contradicting ERP read-back flagged as Conflict — never marked succeeded.

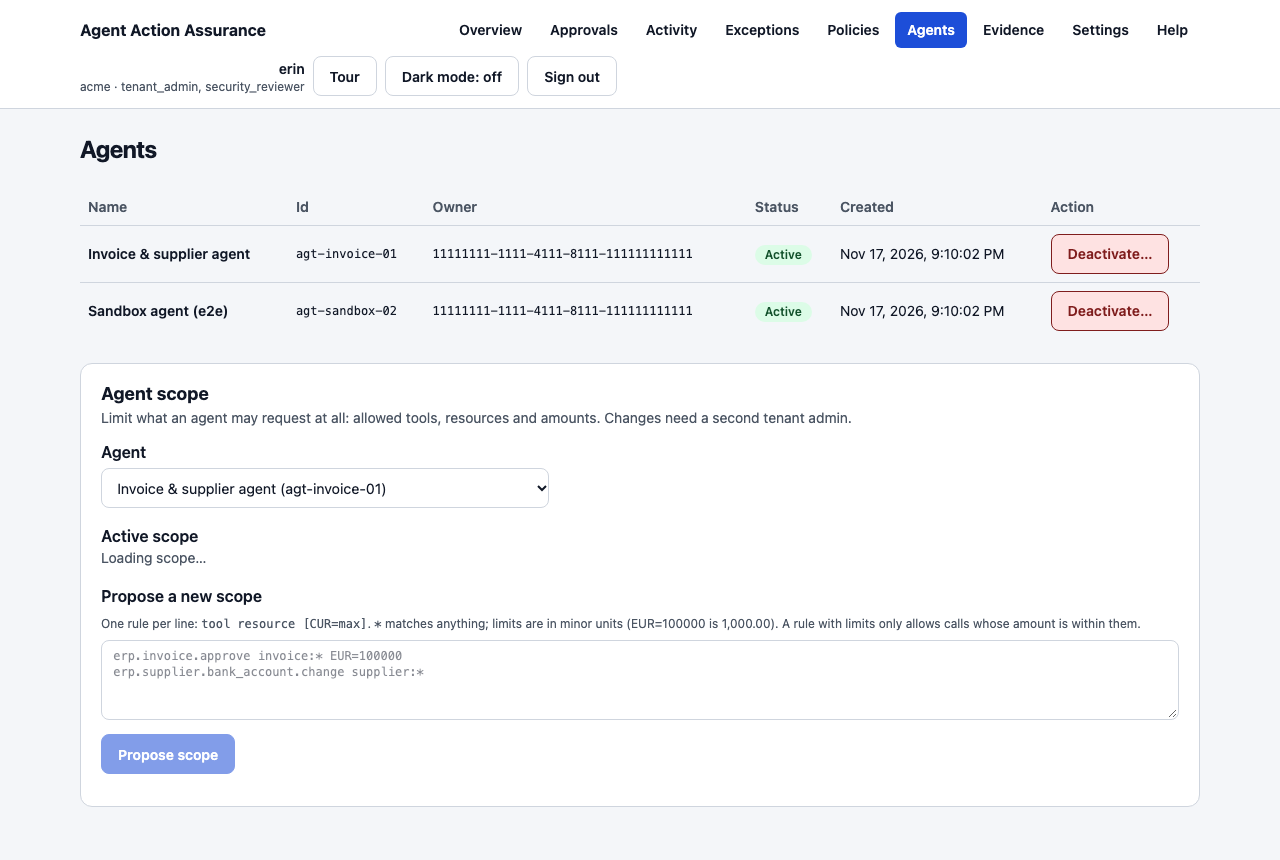
Agent registry and credential management

Agent Registry & Scope

Scoped tool, resource, and currency limits plus kill-switch control.

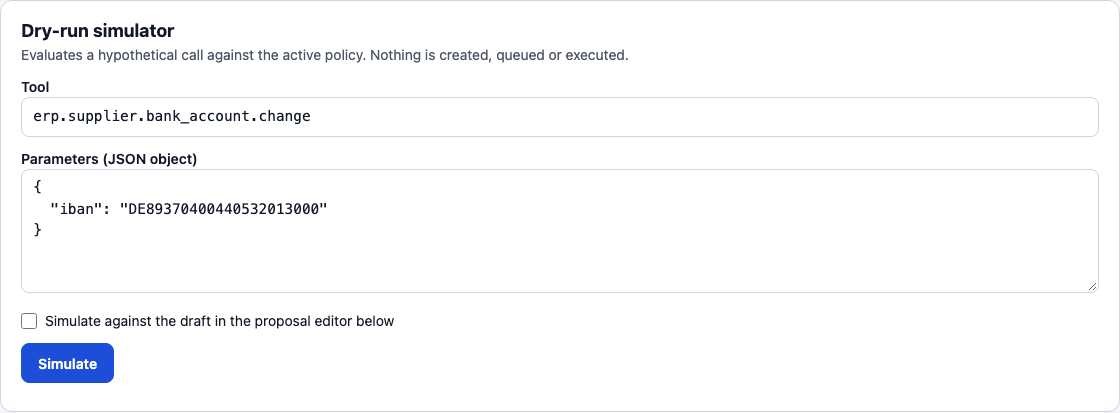
Policy and scope simulator

Policy Simulator

Dry-run policy and agent-scope decisions before activating changes.

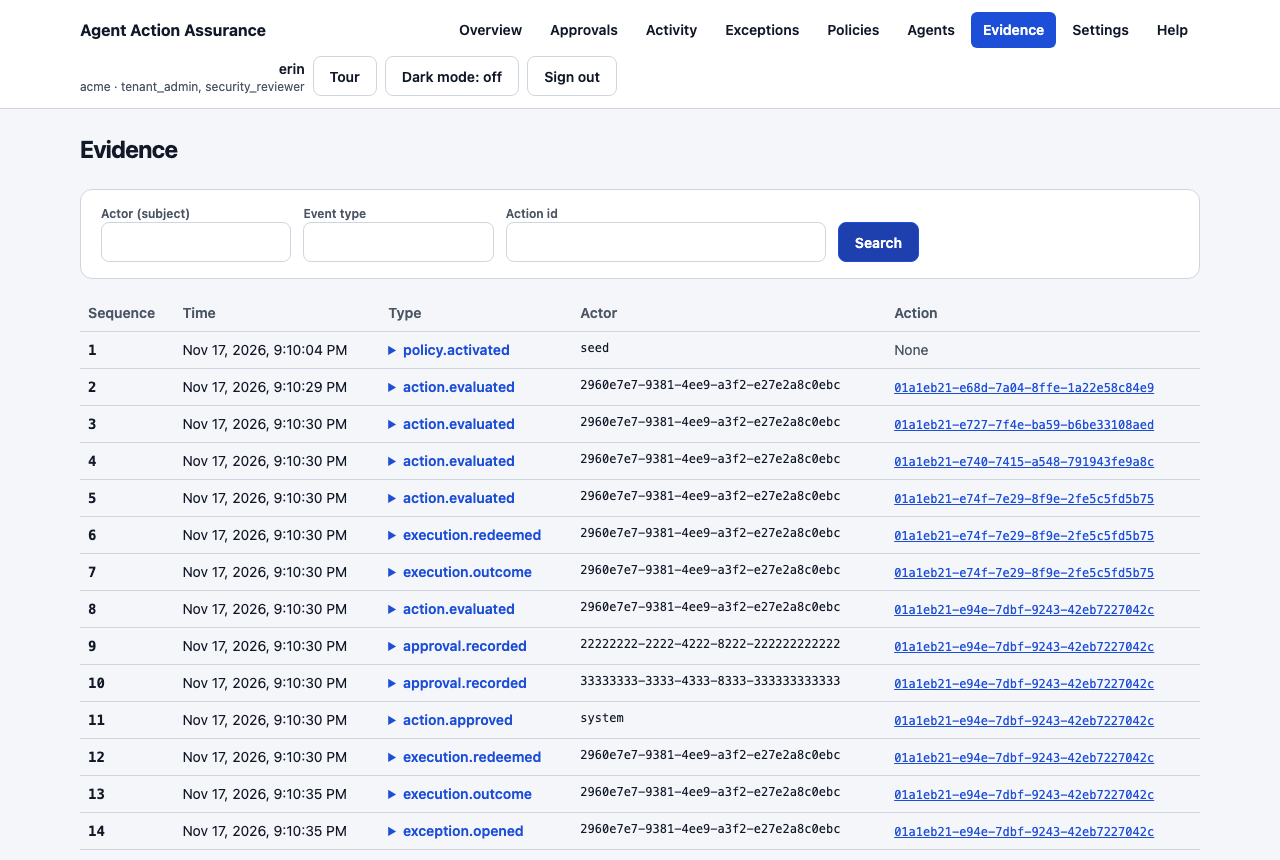
Evidence vault and signed checkpoints

Evidence Vault & Receipts

Tamper-evident hash chain, rotated ECDSA checkpoints, and receipt exports.

Who needs ActEscrow, and who does not.

We qualify out setups where native cloud controls or a simple script cost less.

Consultancy & Mixed-Cloud Onboarding

Built for AI integration consultancies serving multi-client ERP workflows and mid-market engineering teams operating across multiple clouds.

  • Prebuilt verified adapters: Supplier Bank-Account Change & Invoice Approval
  • Deploys alongside Azure, AWS, GCP, Contabo EU VPS, or on-premise workloads
  • 90-day structured pilot path with threat-boundary validation and SOW pack
EnvironmentRecommendationWhy
Mixed-cloud finance/ERP agents (Azure + AWS + legacy ERP)Strong FitSingle deterministic policy, approval inbox, and receipt trail across heterogeneous agent runtimes.
AI consultancies running repeatable client ERP workflowsPrimary ChannelEliminates rebuilding SoD, replay protection, and audit exports per customer.
Microsoft-only (Agent 365 / Entra) or AWS-only (AgentCore)Use Native FirstAdopt native controls first; add an external gateway only for uncovered cross-system transactions.
1–3 read-only internal chatbots or low-risk CRUD scriptsDo Not BuyStandard IAM and logging cost less than introducing an enforcement gateway.

Build or buy? An honest estimate.

If one agent only needs a 1-week internal check, build it yourself. SaaS pays off when multiple runtimes, maker-checker rules, replay protection, and auditor exports become ongoing engineering work.

Illustrative planning math (40h/week, 12 months, excluding cloud infra, procurement, legal, and avoided incident losses).

Year 1: build & maintain in-house

€57,600

€36,000 initial + €21,600 annual upkeep

Year 1: subscription + integration

€14,388

€9,588 license + €4,800 setup & ops

Estimated Year 1 engineering savings: €43,212

Justified when multi-runtime policies, replay safety, and external audit packets create recurring maintenance load.

Priced by governed actions, not by log volume.

Governed workflows, active agents, bounded policy evaluations and explicit retention — never open-ended ingestion.

EUR, pilot hypotheses, excl. VAT.

Developer / Sandbox

€0

Docker Compose & sandbox

Architecture discovery & integration testing

  • Up to 2 enrolled agents & 10k policy evaluations/mo
  • Full Docker Compose stack (Keycloak, Gateway, Control Plane)
  • Canonical digest + SHA-256 hash-chained evidence
  • Offline verification CLI (aa-verify)

No production SLA · local/short retention

Team / Single Workflow

€249

per month · excl. VAT (pilot hypothesis)

First protected finance/ERP action workflow

  • Up to 15 agents · 100k evaluations/mo · 30-day history
  • Dual-control approver inbox with IBAN & invoice parameter diff
  • Maker-checker policy changes (two-admin activation)
  • ERP adapter templates (bank-account change & invoice approval)

€299–€799 pilot range with extra retention/connectors

Partner / Enterprise

€2,500+

custom / month (consultancies €500+ base)

AI consultancies (multi-client) & regulated orgs

  • Customer-owned gateways in Azure, AWS, GCP, Contabo, or on-prem
  • GDPR automated redaction + dual-admin legal hold with cooling-off
  • Dedicated evidence key rotation & WORM / object-lock patterns
  • Pilot SOW, DPA documentation pack & guided onboarding

Custom retention, SLA & annual contract terms

Questions, answered plainly.

Including what we do not do.

All questions
How does a pre-action enforcement gateway differ from prompt guardrails or agent observability?

Guardrails inspect model text and observability records what already happened; the gateway decides on the structured tool call before it reaches the target system.

Full answer
Can an AI agent bypass the gateway and call the ERP directly?

Only if it has its own credential or network route to the ERP. Enforcement holds where the agent has neither; that boundary is a deployment requirement.

Full answer
How does maker-checker separation of duties work for agent actions?

When a rule requires separation of duties, the person who requested the action, or who owns the requesting agent, cannot approve it.

Full answer
Why is step-up MFA checked on the server instead of in the UI?

A UI prompt can be skipped by calling the API directly; the control plane checks the token's acr/amr claims and refuses approvals without them.

Full answer
How is the decision evidence chain different from ordinary logs or a SIEM?

Evidence is a per-tenant SHA-256 hash chain that the application database role can only append to, with ECDSA P-256 signed checkpoints.

Full answer
What is a per-action signed receipt, and what does it prove?

A small signed JSON document (aa.receipt.v1) for one action: its digest, policy, approvals, outcome, observation and evidence hashes. No PII.

Full answer
What happens if the ERP call times out and nobody knows whether it applied?

The action becomes Unknown. It is never blindly retried; the outcome must be reconciled against the target first.

Full answer
What does Conflict mean after an action has executed?

The target accepted the write, but re-reading the record shows a state that contradicts what was approved.

Full answer
When should you not buy ActEscrow?

If your agents are read-only, if you only need prompt filtering, or if a simple approval step for one low-risk workflow is enough.

Full answer

Compare against Microsoft Agent 365, AWS AgentCore, Lakera, OPA and in-house builds.

An eight-alternative capability matrix, and a daily engineering and regulatory journal.

What these guarantees cover — and what they do not

  • The boundary must be non-bypassable: enforcement applies only where the agent has no direct credential or network route to the target system outside the gateway.
  • Integrity is not ground truth: SHA-256 chaining and ECDSA P-256 checkpoints prove recorded bytes were not altered after signing; ERP read-back confirms the target state at execution time, not an agent's reasoning.
  • No premature claims: ActEscrow is an engineering pilot. We do not claim SOC 2, ISO 27001, GDPR certification or guaranteed EU AI Act compliance.